On September 21, 2026, the Office of the Comptroller of the Currency (OCC) published Bulletin 2026-48, updating its Cybersecurity Supervision Work Program (CSW). The update rescinds the 2023 version and realigns the program with Version 2.0 of the NIST Cybersecurity Framework (CSF).
If you’ve worked with the older CSW, the contents should still feel familiar. It just has a new structure. Let's look at five things community banks should know about the refreshed exam procedures.
1. The CSW now aligns with NIST CSF 2.0
The biggest change in this version is the move from NIST CSF v1.1 to NIST CSF v2.0. This change drives almost everything else in the update.
- There’s a new function: Govern. The CSW previously mirrored the five functions from v1.1, which were Identify, Protect, Detect, Respond, and Recover. The updated CSW adds the Govern (GV) function into the mix.
- Governance and supply chain risk moved. In the previous version of the CSW, Governance and Supply Chain Risk Management lived in the Identify function. In the new version, both moved into Govern, which is exactly how NIST reorganized them in v2.0.
- Secure software development has a home. The previous version of the CSW had a “Specialty Area” add-on for secure development because there was no natural category for it. The CSF v2.0 has the Platform Security category in the Protect function, so this content now lives there in the CSW, and the standalone specialty area was removed.
The total number of procedures in the updated CSW is still 89, so this isn’t a bigger program. It’s the same contents but reorganized to better align with the current NIST CSF.
2. The CSW aligns with the FFIEC IT Examination Handbook.
The updated CSW updated its mappings to the FFIEC IT Examination Handbook. Specific booklets that get shoutouts include:
- Information Security (72 references)
- Architecture, Infrastructure, and Operations (43 references)
- Development, Acquisition, and Maintenance (39 references)
- Business Continuity Management (17 references)
- Management (8 references)
- Outsourcing Technology Services (1 reference)
- Development and Acquisition (1 reference)
The mappings include references to specific booklet sections, as well as references to each booklet’s work program.
3. The CSW is not based on the FFIEC Cybersecurity Assessment Tool.
From 2015 to 2023, the OCC's cybersecurity examination program was largely based on the FFIEC Cybersecurity Assessment Tool (CAT). According to the OCC's 2022 Cybersecurity and Financial System Resilience Report to Congress (see PDF page 13), use of the CAT enabled the OCC to:
- "Implement a consistent cybersecurity supervision framework."
- "Monitor and measure cybersecurity preparedness across the federal banking system."
- "Observe the range of practices across banks."
- "Identify common areas of strength and potential control gaps."
- "Better measure the level of preparedness across banks over time."
While the OCC CSW is no longer based on the FFIEC CAT (which sunset in August 2025), alignment with the NIST CSF enables the OCC to continue to meet these objectives using another common framework .
4. The CSW is mapped to several industry frameworks.
One of my favorite parts about the CSW is the Cybersecurity Supervision Work Program References tool. This tool is designed to give banks a way to map the CSW statements to existing guidance and frameworks, such as the CIS Controls, CRI Profile, and the NIST SP 800-53 controls.
Here's an example of what the tool looks like.
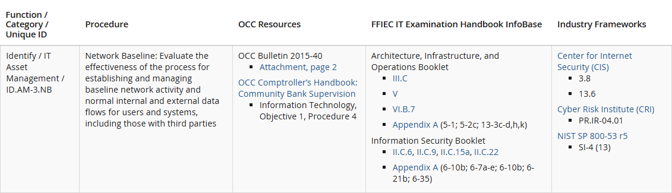
This is a win-win. It's helpful for OCC examiners who may want to learn more about a certain topic, and it's helpful for banks when preparing for an upcoming examination, regardless of the framework they use for their cybersecurity control self-assessments.
5. The CSW can be used as a cybersecurity framework.
Since the FFIEC CAT sunset, many financial institutions have transitioned to alternate frameworks, with some even asking, "Can I use the CSW as a cybersecurity framework?"
The short answer is: Maybe. It depends on how you want to use it.
- Pros: The CSW offers a structured, process-oriented way to review your cybersecurity program, identify gaps, and prepare for upcoming examinations. Its consistent approach and useful mappings can help you establish a repeatable self-assessment routine for continuous improvement.
- Cons: Like many modern cybersecurity frameworks, the CSW is not a checklist of controls. Most of the procedures begin with verbs like "evaluate," "review," or "determine." This indicates the CSW is intended for use by someone reviewing a cybersecurity program, not someone implementing one. If you are looking for more prescriptive guidance, pairing the CSW with another framework may provide deeper coverage.
OCC Bulletin 2026-48 addresses this question directly by saying:
“The CSW does not establish new regulatory expectations, and banks are not expected to use this work program to assess cybersecurity preparedness. The OCC continues to encourage, but does not require, the use of a standardized approach to assess and improve cybersecurity preparedness, and banks may choose from a variety of tools and frameworks available.”
In Summary
The OCC CSW program is a helpful tool for both community banks and examiners to use when assessing cybersecurity preparedness. While the CSW update does not significantly change the program, it does align it with the current version of the NIST CSF and provides helpful references to other industry frameworks. Visit the OCC’s website to access the latest version of the CSW or use the CSW in Tandem Cybersecurity Assessment.
Use the OCC CSW in Tandem
Tandem makes it easy to complete cybersecurity control self-assessments using common frameworks, including the NIST CSF and the OCC CSW. Our web application streamlines the process with helpful assessment tools, easy-to-access reporting, downloadable documents, peer benchmarking, notifications, and more.
Sign up and get started for free at Tandem.App/Cybersecurity.

Frequently Asked Questions (FAQs)
What is the OCC Cybersecurity Supervision Work Program (CSW)?
The CSW is a set of high-level examination procedures OCC examiners can use to assess a bank’s cybersecurity preparedness. It aligns with the NIST Cybersecurity Framework and maps to the FFIEC IT Examination Handbook and common industry frameworks.
What changed in the 2026 update to the OCC CSW?
OCC Bulletin 2026-48 announced the realignment of the OCC CSW with the NIST CSF v2.0. The biggest change is the new Govern function, which now houses the governance and supply chain procedures that previously lived in the Identify function. The number of procedures stayed at 89.
Does the OCC CSW align with the NIST CSF 2.0?
While the procedures do not match verbatim, the current version of the OCC CSW does mirror the six CSF 2.0 functions (Govern, Identify, Protect, Detect, Respond, and Recover) and the procedures generally align with CSF outcomes.
Are banks required to use the OCC CSW?
No. The OCC states the CSW sets no new regulatory expectations and that banks are not expected to use it to assess their own preparedness. It is primarily an examination tool, although banks can use it to perform cybersecurity control self-assessments and prepare for exams.
Can I use the OCC CSW as a cybersecurity framework?
Yes, you can use it to review and self-assess your program, and the framework mappings make it useful for exam prep.
Update Log:
- 10/08/2025: Removed obsolete FFIEC references; added considerations for using the CSW as a framework.
- 10/15/2026: Updated the article contents to reflect the OCC’s most recent update to the CSW and the Cybersecurity Supervision Work Program References tool.